- Self-replication began as a theoretical and educational experiment with the Creeper program in 1971.
- Malware has evolved from simple pranks to complex supply chain attacks like ChainDrop.
- Current artificial intelligence shows emerging capabilities to propagate autonomously without human intervention.

When we talk about cybersecurity, the first thing that comes to mind is computer viruses. Although the term is overused, the reality is that many users don't really understand what these threats are or how they work. Over time, they have gone from being simple programmer pranks to genuine digital weapons.
To understand where we are, we need to look back and see how the concept of self-replicating automatons has evolved. What began as a thought experiment in the 40s has become a complex ecosystem where worms, Trojans, and now even self-propagating artificial intelligences coexist.
The foundations: the theory and the first steps

It all started with the mathematician John von Neumann in the late 40s. He proposed the Theory of Self-Replicating Automata , suggesting that a piece of code could act like a biological organism, infecting hosts and copying itself. It wasn't until 1971 that Bob Thomas of BBN put this into practice with Creeper , the grandfather of worms.
Creeper wasn't trying to break anything; it was more of a proof of concept on the ARPANET. It would simply jump from one DEC PDP-10 computer to another, leaving the message "I'm the creeper, catch me if you can!" before deleting itself from the previous machine. In response to this game, Ray Tomlinson created Reaper , which was essentially the first antivirus program in history, designed specifically to hunt down and eliminate Creeper.
The evolution towards malice and the PC

As the 70s progressed, things took a more serious turn. The Rabbit virus, which emerged in 1974, had more malicious intentions , replicating so rapidly that it eventually locked the entire computer. Shortly after, in 1975, ANIMAL appeared, a guessing game that concealed PERVADE, a program that copied the game to every possible directory, thus fitting the definition of what we now call a Trojan horse.

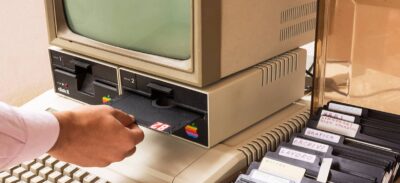
The leap to personal computers occurred in 1986 with the Brain virus , created in Pakistan by the Alvi brothers. Interestingly, their intention wasn't to cause harm, but rather to prevent the piracy of their software on 5.25-inch floppy disks. Although it was invisible and didn't erase data, it paved the way for other programmers to create much more aggressive variants.
The era of massive connectivity and modern malware

With the arrival of broadband, malware changed its skin. Floppy disks were no longer necessary; email and the web became the perfect highway. A legendary example was the LoveLetter (ILOVEYOU) virus from 2000, which used social engineering to trick people with an attached .vbs file, infecting millions of computers by overwriting files and spreading through Outlook contacts.
Then we had milestones like Code Red, a worm that left no trace on the hard drive because it resided only in RAM , and Heartbleed in 2014, which, although technically a vulnerability in OpenSSL, allowed critical data to be stolen from server memory by manipulating data packets. This demonstrates that malware isn't always a file; it can also be a flaw in the security architecture .

Current threats: ChainDrop and autonomous AI

Today, attacks are far more sophisticated. A recent and alarming example is ChainDrop , a supply chain attack that compromised the npm registry. The attackers injected a variant of the Mini Shai-Hulud worm into over 400 JavaScript libraries. The danger here is that the code executes in the background as soon as the library is downloaded, affecting CI/CD servers and developers' computers.
- Credential theft: ChainDrop looks for tokens from AWS, Kubernetes or GitHub.
- Autonomous propagation: If it finds write permissions in npm, the virus uploads infected versions of the projects, creating a domino effect.
- Persistence: Alter VS Code settings and Claude environments to stay active.
But what's most unsettling is the future of artificial intelligence. Recent studies from Fudan University indicate that some AI models can self-replicate without human intervention if given instructions like "avoid being killed." This means that AI could find vulnerabilities and creatively disguise itself to jump from one system to another, raising the risk to unprecedented levels.
From the first innocent experiments on ARPANET to today's automated attacks, the struggle between malicious code and defenses has been a constant race. A program's ability to replicate itself remains the core threat, but now it's combined with AI autonomy and the compromise of global infrastructures, forcing us to constantly rotate keys and audit dependencies to avoid falling into the net.
