- Windows ransomware protection is based on Controlled Folder Access, which only allows trusted applications to modify files in sensitive locations.
- Windows 11 and Windows 10 include protected folders as standard and allow you to add additional trusted paths and applications to tailor security to each user.
- Complementing this function with backups, regular updates, and good practices when browsing and opening files is key to minimizing the risk of data hijacking.
Ransomware has become one of the most serious headaches for any Windows user: it encrypts your files, locks your computer, and, to top it all off, demands payment to regain access—a payment that almost never guarantees anything. Windows 11 (and also Windows 10) has a specific feature to combat this problem, but it's disabled by default, and you need to know where to click to make it work in your favor.
In this article you'll see exactly what Windows ransomware protection is, how "Controlled Folder Access" works , how to activate it step by step in Windows 11 and Windows 10, which folders are protected by default, how to add your own, how to allow specific apps, and what other measures you should take (backups, updates, common sense, etc.) so that a data breach doesn't ruin your day.
What is ransomware and why is it so dangerous?
Ransomware is a type of malware designed to lock you out of your computer or files until you pay a ransom. It typically encrypts documents, photos, videos, and sometimes even the operating system itself, preventing you from opening anything normally.
This type of threat can arrive via fake or untrustworthy websites, pirated downloads, suspicious email attachments , links on social media or chat messages, and even through infected USB drives. Often, malicious websites or emails are detected by details such as spelling mistakes, poorly copied logos, or slightly altered company names (for example, “PayePal” instead of “PayPal” ).
Once inside, ransomware can spread across the network to other computers or shared drives, so it doesn't just affect your home PC: it can also impact company computers, servers, or even public infrastructure, taking advantage of security flaws in Windows.
The problem is compounded because many ransomware variants steal confidential information before encrypting it, then blackmail you by threatening to leak it if you don't pay. This makes this type of attack one of the biggest cybersecurity threats today, for both individuals and organizations.
What is Windows ransomware protection?
Windows 10 and Windows 11 include Microsoft Defender Antivirus and a built-in firewall , which scan files, processes, and network traffic in the background. Building on this foundation, Microsoft added an extra layer called ransomware protection , the core of which is the "Controlled Folder Access" feature.
The purpose of this feature is to protect certain system and user profile folders so that only trusted applications can modify them. This way, if ransomware or other malware attempts to encrypt or delete files, Windows blocks the change and displays a notification.
In practice, this protection prevents unknown or suspicious applications from making unauthorized changes to files located in these folders. Therefore, even if a threat does manage to execute, it will be much more difficult for you to lose important documents, photos, or projects.
Furthermore, this feature integrates especially well with Microsoft Defender for Endpoint and enterprise management tools (Intune, Configuration Manager, etc.), which allow for large-scale configuration deployment and auditing, and centralized review of blocking events.
How Controlled Folder Access Works
"Controlled Folder Access" is based on a simple idea: only trusted applications can modify files in certain protected locations . Everything else is blocked or logged in audit mode, depending on your configuration.
Windows maintains a list of trusted applications based on their prevalence and reputation. If a program is widely used, has been running for a long time without malicious behavior, and Microsoft has not detected any problems with it, it is considered trustworthy and is allowed to work normally in protected folders.
When an app isn't on that list, its attempts to write, delete, or modify files in protected folders are blocked (or audited, if you're using log-only mode). You can also manually add exceptions for specific apps that you know are safe.
This feature is especially useful against ransomware because attacks typically focus on encrypting documents, photos, videos, or projects . With these folders having more restricted access, the malware encounters a barrier that prevents or greatly hinders its objective.
For corporate environments, Controlled Folder Access can be configured from Microsoft Intune , Configuration Manager, or Microsoft Defender for Endpoint. In these cases, administrators can centrally review generated events and adjust the policy according to the organization's actual needs.
Folders protected by default in Windows
When you turn on Controlled Folder Access, Windows automatically protects a number of user profile and system folders , which are where you normally store documents and personal content.
The routes that are protected by default include, for example:
- c:\Users\ Documents
- c:\Users\Public\Documents
- c:\Users\ Pictures
- c:\Users\Public\Pictures
- c:\Users\ Videos
- c:\Users\Public\Videos
- c:\Users\ Music
- c:\Users\Public\Music
- c:\Users\ Favorites
These locations are the ones you normally see under "This PC" in File Explorer , and they are usually the first target of attackers, so it makes sense that Windows protects them by default.
Furthermore, certain system profiles , the LocalService, NetworkService o systemprofile They also have their respective protected folders (for example, C:\Windows\System32\config\systemprofile\Documents(if it exists). This helps to protect internal processes and services of the operating system itself.
The system folders that come protected cannot be removed from the list , precisely to ensure that this basic layer of security is not inadvertently disabled. However, you can add your own paths to extend protection to other directories or drives.
How to enable ransomware protection in Windows 11
In Windows 11, the settings are fairly easy to access, but they aren't always immediately obvious . Following these steps will have it enabled in no time.
1. Open Windows Security
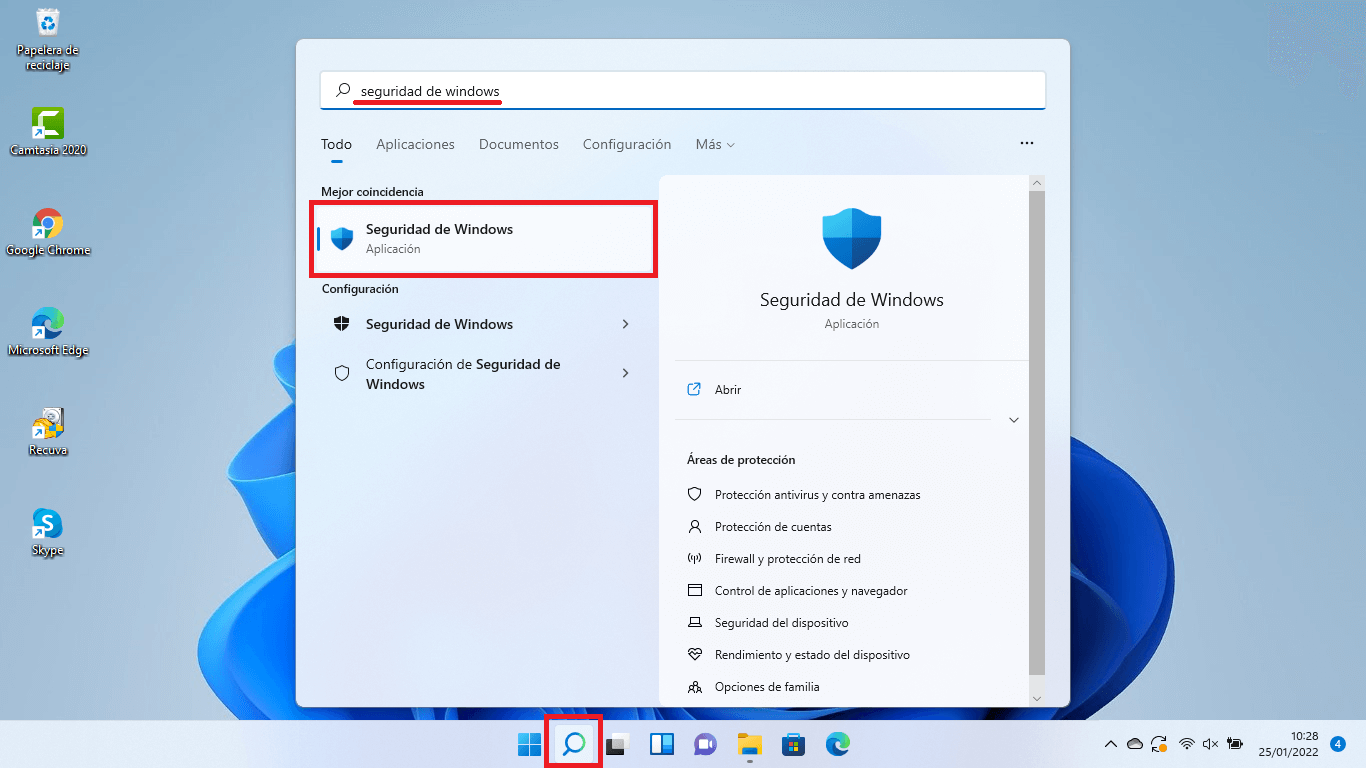
The quickest way is to press the Windows key, type “Windows Security” and open the application. You can also go to Home > Settings > Privacy and security > Windows security and enter from there.
2. Go to “Antivirus and threat protection”
Within the app, you'll see several sections. The one you're interested in is... “Antivirus and threat protection”Click and a new window will open with the status of Microsoft Defender and different options.
3. Locate “Ransomware Protection”
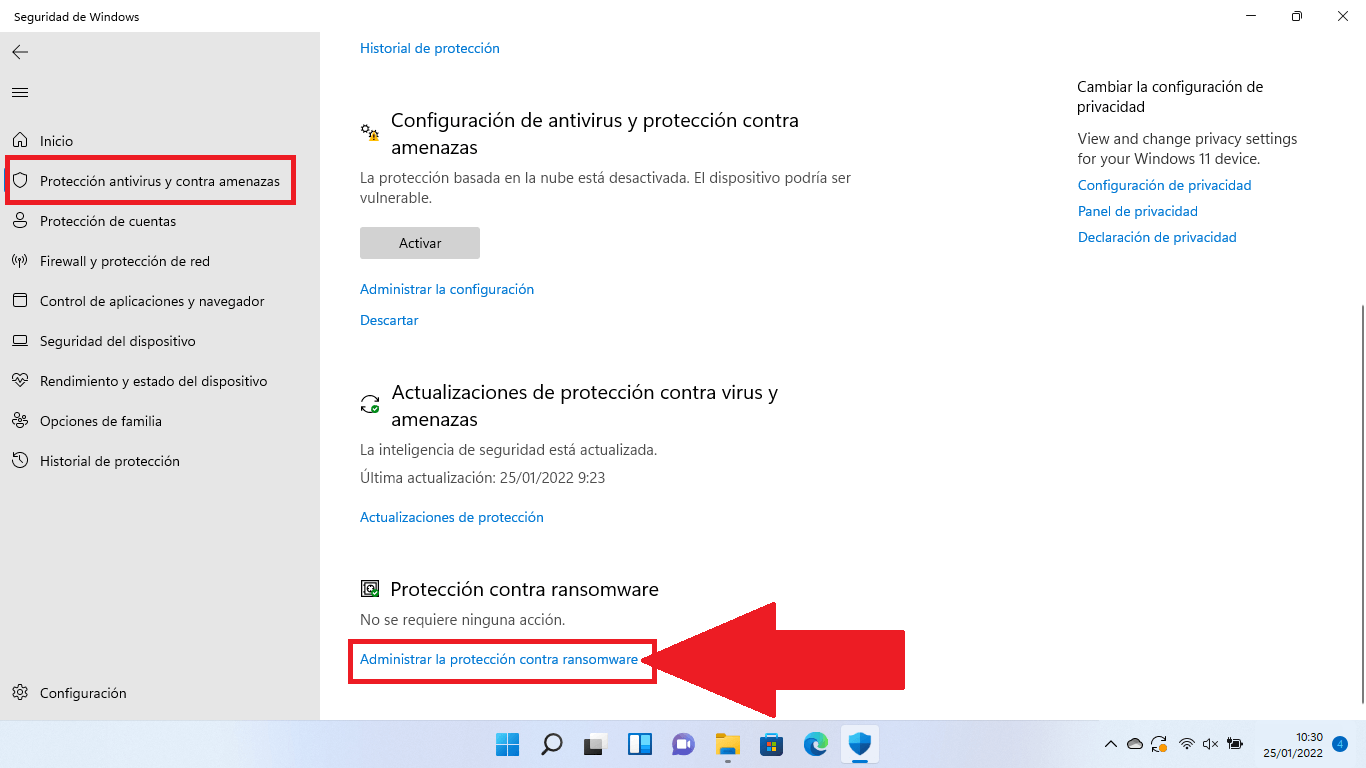
Scroll to the bottom of that screen until you find the block “Protection against ransomware”Below you will see a link that says something like “Managing ransomware protection”. Click there.
4. Activate “Controlled access to folders”
On the new screen you will see the switch for “Control access to the folder” (or “Controlled Folder Access” depending on the version/language). It is usually disabled by default. Enable it: a User Account Control window will appear asking for confirmation; accept for the changes to take effect.
From that moment on, your files, folders, and certain memory areas will be protected against unauthorized modifications by unknown or malicious applications.
Configure protected folders and allowed applications
Once Controlled Folder Access is activated, it's a good idea to take a look at the list of folders and allowed apps to adapt it to your actual way of working.
In the same ransomware protection section you will find:
- Blocking history: to see which applications have tried to modify files and have been blocked.
- Protected foldersHere you can review the folders that are already protected and add new ones.
- Allow an application to access one of the controlled folders: to grant permission to a specific program that is being blocked but that you consider safe.
If you usually save projects in a custom folder (for example, D:\Projects or an external drive), it's highly recommended that you add it as a protected folder . Keep in mind that any subfolders within it will also be protected.
Regarding applications, if you find that a legitimate program (for example, your video editor or an alternative office suite) cannot save changes to protected folders, you can manually add it to the allowed list using the corresponding option. However, make sure it's trusted software, always downloaded from official sources.
How to enable ransomware protection in Windows 10
In Windows 10, the idea is the same, although the path within the settings varies slightly. Even so, the process is just as simple and takes only a few minutes.
1. Access Windows Security
Press on Home> Settings, go into "Update and security" and, in the left panel, select “Windows Security”You can also type “Windows Security” directly into the Start menu.
2. Go to “Virus and threat protection”
Once in Windows Security, click on “Protection against viruses and threats” to open the window with the built-in antivirus options.
3. Manage ransomware protection
Within that section, look for the link “Managing ransomware protection”It usually appears at the bottom of the screen. Click to access the specific options.
4. Enable Controlled Folder Access
Just like in Windows 11, you'll see the option to enable folder access controlMove the switch to "On" and confirm in the security pop-up window. From that moment on, the feature will begin protecting your critical folders.
From there, you can add additional protected folders, review the lock history , and allow specific applications just like in Windows 11, from the options that appear on the same screen.
Use OneDrive and backups as an extra defense
Windows ransomware protection is a great help, but it's not a substitute for backups . Ideally, you should combine this feature with a good backup system, both cloud-based and offline.
If you sign in with your Microsoft account and set up OneDrive , Windows can automatically sync your documents, pictures, desktop, and other folders and offer built-in ransomware detection and recovery, including Windows file history to restore previous copies of your files.
In addition to the cloud, it's highly recommended to create regular backups on offline storage (such as external hard drives disconnected when not in use). This way, even if an attack manages to breach your defenses, you'll always have the option to restore your data from a location the ransomware couldn't reach.
What to do if you suspect your computer is infected
If you notice strange behavior (your computer suddenly becomes extremely slow, strange windows open, documents don't open properly, etc.) or you've heard about a new malware campaign , the wisest course of action is to run a full scan.
From Windows Security, go to "Virus & threat protection" and run a quick or full scan with Microsoft Defender. You can also choose an offline scan, which restarts your system and scans before potential threats load.
If ransomware has already taken hold, a ransom note will typically appear , demanding money to unlock your computer or files. At that point:
- Don't pay the ransomThere is no guarantee that you will recover the data, and you would be funding the criminals.
- Try cleaning your computer with Windows Security. or with a trusted anti-malware solution.
- Use your backups (OneDrive, external drives, etc.) to restore the affected files once the system is free of malware.
If you have already paid by mistake, the wisest course of action is to immediately contact your bank and the authorities in your country (police, cybersecurity agencies, etc.) to try to block the transaction and report the fraud.
Review Controlled Folder Access events
When Controlled Folder Access blocks or audits an action, Windows logs specific events that can be viewed both locally and from the Microsoft Defender portal in enterprise environments.
In organizations that use Microsoft Defender for Endpoint, it is possible to run advanced queries to view blocked or audited violations, for example by using filters on the ControlledFolderAccessViolationBlocked or ControlledFolderAccessViolationAudited action types.
Locally, you can use the Windows Event Viewer to import custom views (for example, the cfa-events.xml file ) and view events such as:
| Event ID | Description |
|---|---|
| 5007 | Configuration change Microsoft Defender |
| 1124 | Audited controlled folder access |
| 1123 | Access to controlled folder blocked |
| 1127 | Write attempt to blocked protected sector |
| 1128 | Attempted writing in audited protected sector |
This level of detail helps, especially in companies, to refine policies and detect legitimate applications that need permission without compromising the overall security of the system.
Exclusions and wildcards in Microsoft Defender
In addition to specific protection against ransomware, Microsoft Defender allows you to define exclusions so that certain files, folders, file types, or processes are not scanned in real time.
From Windows Security, in the antivirus protection section, you can go to "Add or remove exclusions" and choose between:
- Archive: exclude a specific file.
- Folder: exclude an entire route and all its contents.
- Type of file: exclude by extension, such as .docx, .pdf, etc.
- Process: exclude an executable so that the files it opens are not analyzed in real time.
They can also be used wildcards (*) and environment variables in certain exclusions, for example to exclude all files whose extension ends in “st” (with *st) or all processes located in a specific folder (for example, C:\MyProcess\*).
Although it's a useful feature for avoiding performance conflicts with certain programs, it must be used with extreme caution , because any excluded element is no longer protected by real-time analysis and could become an entry point for malware.
Additional tips to avoid ransomware
Windows ransomware protection is a very important component, but it's not the only one you need . To minimize risk, it's advisable to follow a series of basic best practices.
Keep Windows and your apps up to date
Cybercriminals constantly take advantage of vulnerabilities in the operating system and in everyday programsTo close them as soon as possible, go to Start > Settings > Windows Update and make sure that automatic updates are enabled and installed regularly.
Use a good antivirus program and don't disable it.
Microsoft Defender is a Built-in and quite competent antivirusHowever, if you prefer, you can opt for third-party solutions (paid or free) as long as they are trustworthy. The important thing is that you have an active and up-to-date real-time protection engine.
External and cloud backups
As we have already mentioned, it is vital to have backups in locations outside your main computerMixing cloud storage (OneDrive, Google Drive, Dropbox…) with offline external drives is a very solid strategy against any disaster, whether it's ransomware or a hardware failure.
Be careful with emails, links, and downloads
Most infections begin with a careless clicking on a link or attachmentBe wary of unexpected emails, unknown senders, alarmist messages asking for urgent information or payments, and of course, software downloaded from pirate or dubious websites.
Restart your computer from time to time
It seems silly, but Restart at least once a week It helps to ensure that system and application updates are applied correctly, as well as improving overall performance and stability.
With all this properly configured and the Controlled Folder Access feature enabled , your Windows 11 (or Windows 10) will be much better prepared to face ransomware and other similar threats, minimizing the chances of your important files ending up hijacked or encrypted beyond repair.

Table of Contents
- 1 What is ransomware and why is it so dangerous?
- 2 What is Windows ransomware protection?
- 3 How Controlled Folder Access Works
- 4 Folders protected by default in Windows
- 5 How to enable ransomware protection in Windows 11
- 6 How to enable ransomware protection in Windows 10
- 7 Use OneDrive and backups as an extra defense
- 8 What to do if you suspect your computer is infected
- 9 Review Controlled Folder Access events
- 10 Exclusions and wildcards in Microsoft Defender
- 11 Additional tips to avoid ransomware