- VPNs create an encrypted tunnel that protects your data and can be used both for remote access and to improve your online privacy.
- Windows 10 and 11 allow you to configure built-in VPN profiles and set up your own VPN server without third-party programs.
- For a home VPN to work properly, you need to open port 1723 on the router and allow Routing and Remote Access in the firewall.
- A commercial VPN service simplifies setup, offers servers in many countries, and adds extra security and convenience features.
Setting up a VPN on Windows might seem complicated at first, but with a good guide, it becomes quite manageable. Whether you want to protect your privacy on public networks or need to connect to your company's network from home, Windows includes built-in tools for creating and using VPN connections without always relying on external programs.
Throughout this article you will see, step by step, how to set up a VPN on Windows 10 and Windows 11 , how to set up your own VPN server at home, what settings to adjust on your router and firewall, and also how to use commercial VPN services when you want to virtually change countries or add extra layers of security and convenience.
What is a VPN and what types can you use on Windows?
A VPN (Virtual Private Network) is, simply put, an encrypted tunnel within the internet that connects your device to another computer or network as if you were physically there. This tunnel protects your data from prying eyes, unsecured Wi-Fi networks, and certain types of tracking.
When you connect to a VPN, your traffic first goes to the VPN server , is encrypted, and travels through that secure tunnel. The VPN server communicates with the websites and services you visit, so they only see the server's IP address, not your home router's or the public network's IP address.
In the Windows environment, it is important to distinguish between two approaches: using a built-in or corporate VPN (for example, to access your company network or your home network) and using a commercial VPN service (NordVPN, ExpressVPN, AVG Secure VPN, etc.), designed to browse anonymously, bypass geographical restrictions, and enhance your privacy.
With Windows' built-in VPN, you can connect to a specific network you already know , such as your work or home network, but your public IP address will remain the one provided by your internet service provider. With a paid VPN service, on the other hand, you use IP addresses from servers distributed around the world , allowing you to simulate being in another country and benefit from IP addresses shared with other users.
A home or business VPN is typically more focused on remote access to internal resources (folders, servers, printers, or PCs) and encrypting traffic between your device and that specific network. A commercial VPN service is more geared towards general online privacy , bypassing blocks, and hiding your real IP address from websites, advertisers, and potential attackers on open networks.
What is the purpose of a home VPN on Windows?
When people talk about VPNs, many only think about "making it appear as if I'm in another country to access certain content," but setting up your own VPN on Windows has other uses. A home VPN alone won't allow you to appear as if you're browsing from another country if your server is in Spain; websites will still see that you're accessing the site from Spain, even if they don't see your real home IP address.
The main advantage of setting up your own VPN server is that all your traffic is encrypted from your device to that server . This means that in a coffee shop, hotel, or airport, anyone trying to spy on the network will see unreadable data because your connection is encapsulated within the VPN tunnel.
Furthermore, by using your VPN server as an intermediary, websites no longer store your router's IP address or the public network's IP address, but rather the IP address of the VPN server you connect to. This makes it more difficult for apps, advertisers, or other third parties to track your movements between different services and correlate exactly which websites you've visited.
Every time you open a webpage, what actually happens is that your browser sends a request to the server hosting that website. That server responds using your IP address as your "digital postal address." Without a VPN, all websites accumulate your IP address in their logs , which they can then share or sell to advertisers to profile your online activity.
By using a VPN, the VPN server, not your computer, is the one actually communicating with the web server . Therefore, websites store the VPN server's IP address, not yours. This is a simple way to reduce your online footprint, especially if you manage the server yourself or trust the person who manages it.
Another interesting advantage of having your own VPN server is that you can set up a kind of extended local area network (LAN ). This means your devices can behave as if they were on the same LAN even if they are physically in different locations, making it easier to share internal resources, access a home PC from work, or avoid some of the physical cabling if everything is on the same logical network.
How to create and configure a VPN profile in Windows 10 and Windows 11
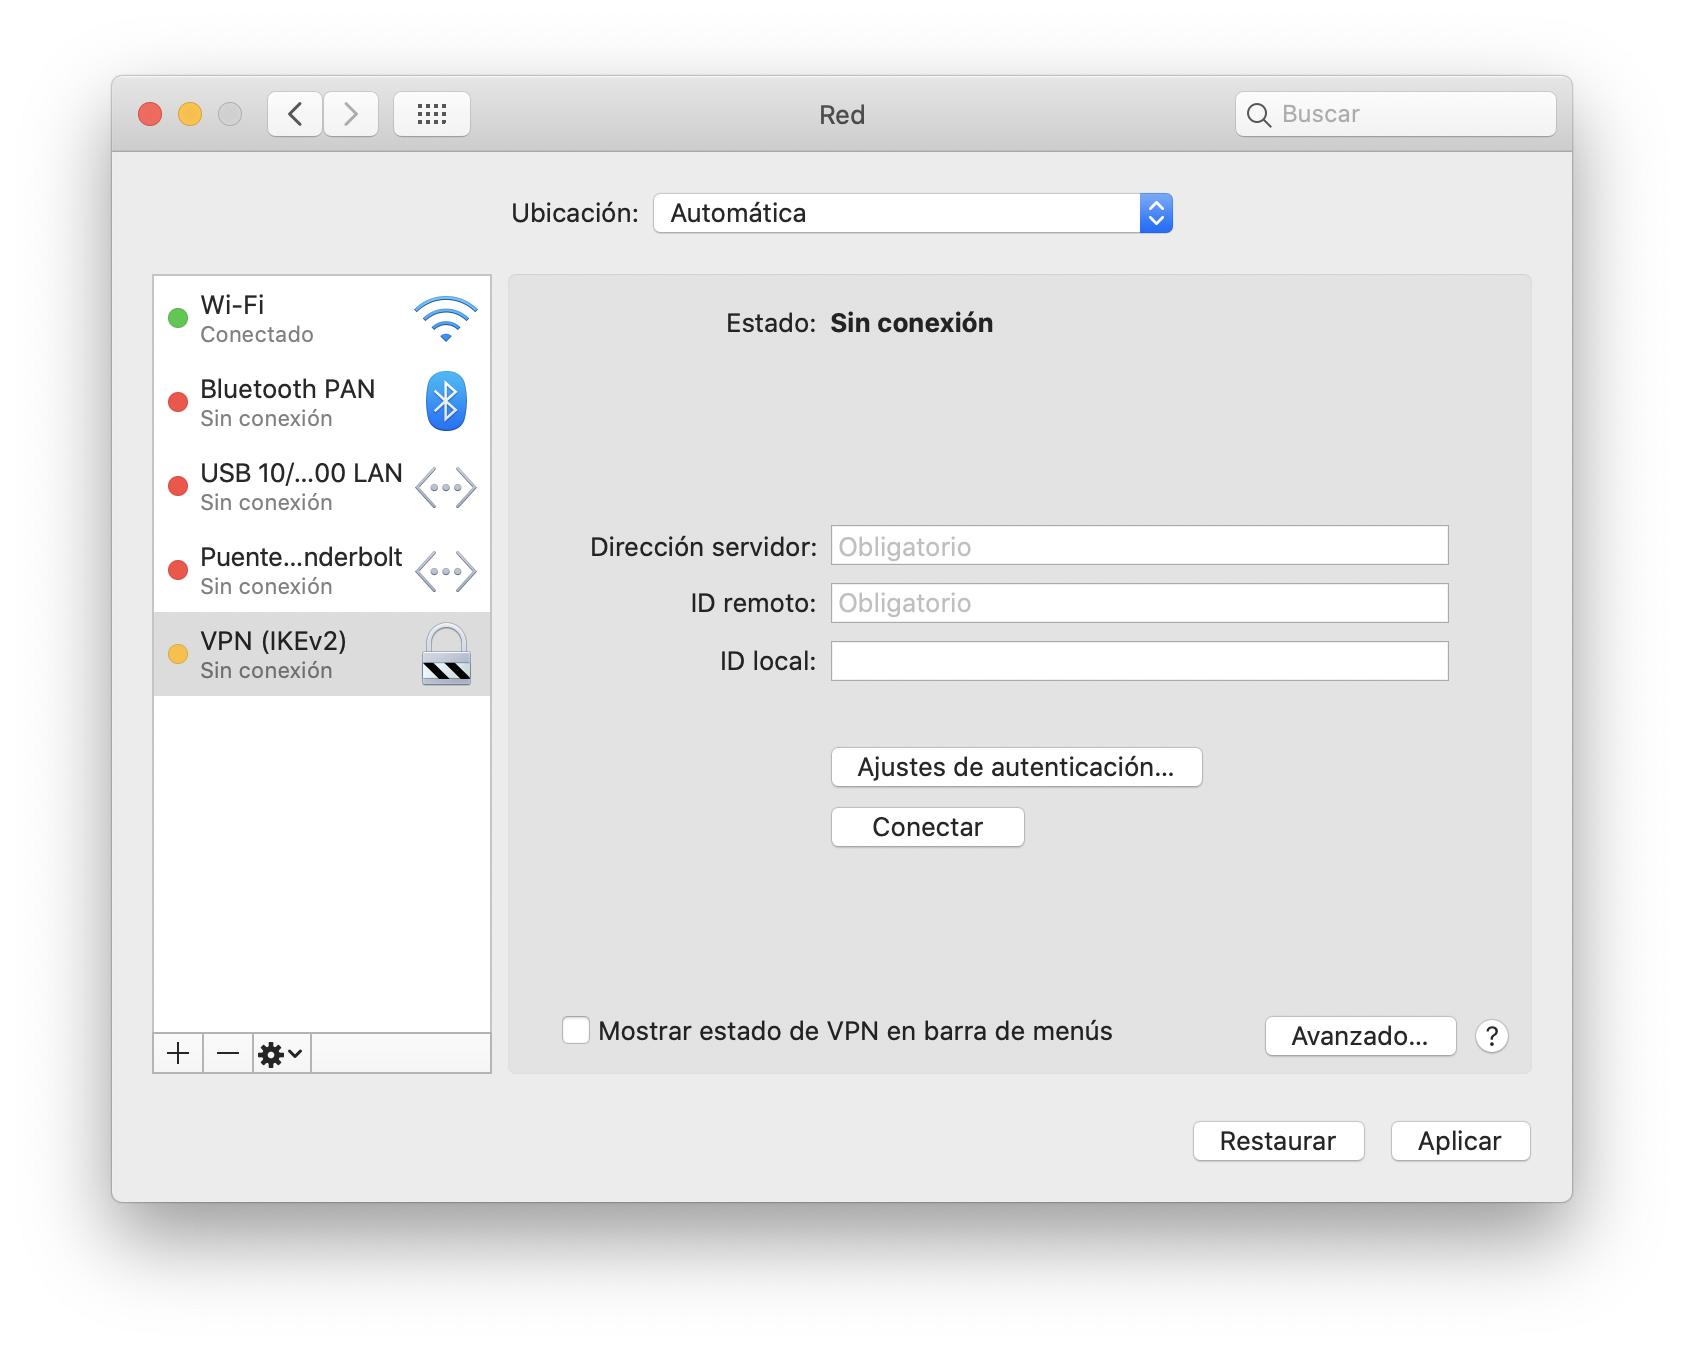
Before you can connect to a VPN on Windows, you need to have a VPN connection profile created . This profile includes the VPN type, server address, authentication method, and, if necessary, username and password.
If the VPN is for work, your company will usually provide you with all the connection details or even its own application. In that case, it's generally a good idea to access the corporate intranet or speak with the IT department to get precise instructions, as each company has its own security policy.
If you want to use a third-party VPN service for personal use, you can first look for its app in the Microsoft Store or on its official website . They almost always offer a Windows client that configures everything automatically. If you prefer to do it manually, their help page usually lists the server addresses, supported protocols, and other parameters.
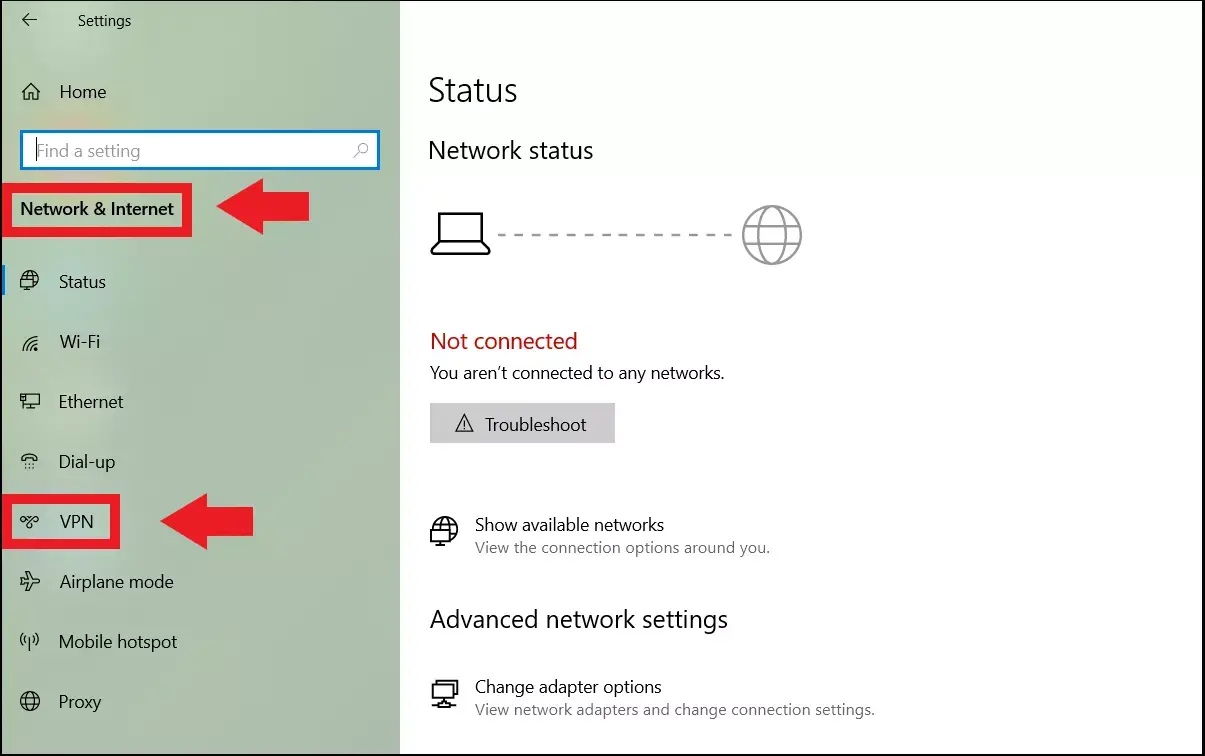
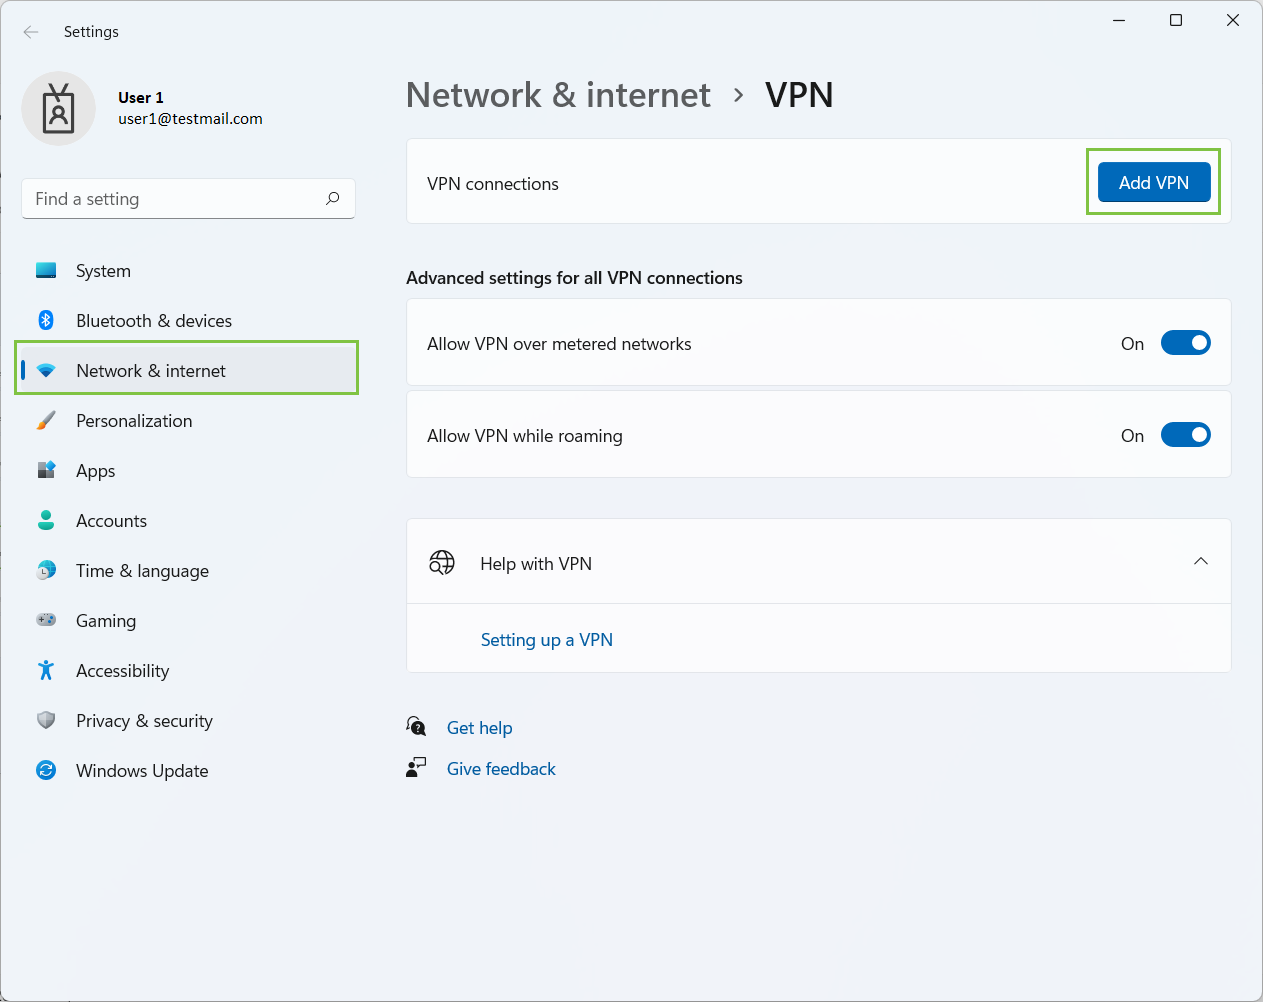
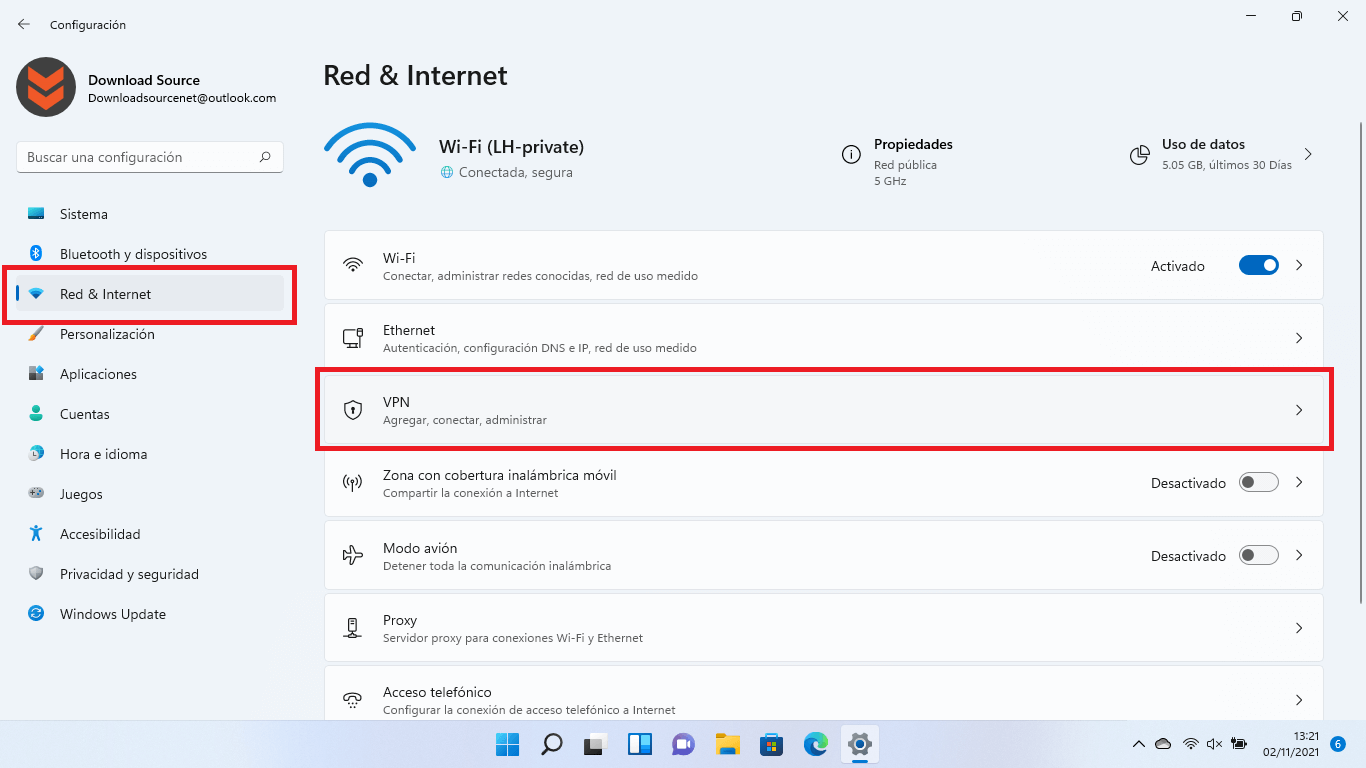
Once you have your VPN details (whether for work, home, or a third-party provider), it's time to create the profile in Windows. In Windows 11, you can open the Settings app and go to Network & Internet > VPN > Add VPN . In Windows 10, the path is very similar: also go to Settings, then Network & Internet, and look for the VPN section.
In the "Add a VPN connection" form, in the provider field, you should select "Windows (built-in)" if you're using the system's native functionality. Then, enter a connection name that you'll easily recognize (for example, "Home VPN" or "Business VPN") and note the IP address or DNS name of the VPN server you'll be using in the server or address field.
In the VPN type section, you'll need to choose the protocol or connection method used by your server or the service you've subscribed to. Windows supports several types, so it's crucial to know which VPN the other party supports . If you're unsure, check your company's or VPN provider's documentation.
In “Login information type,” you can select whether to use a username and password, certificate, one-time token, or smart card . For corporate connections, certificates or strong authentication methods are commonly used. If you need to enter a username and password, you can save them directly in the available fields or leave them blank so you are prompted for them each time.
Once you have everything set up, save the profile. If you need to review or adjust anything later, you can return to the VPN section in Settings, select the connection, and go to Advanced Options . From there, you can change parameters, configure a proxy, or delete the profile if you no longer need it.
Once the profile is created, connecting is very simple: at the far right of the taskbar, above the Network icon (WiFi or Ethernet), you'll see the list of available VPN connections . Choose the one you want, click Connect, enter your credentials if prompted, and if everything is working correctly, the status will change to "Connected".
While connected to a recognized VPN, a small blue shield or similar indicator will usually appear in the network area, and on the VPN settings page you'll see the text "Connected" under the connection name. This allows you to quickly verify whether the VPN tunnel is active.
How to set up your own VPN server on Windows 10 or 11
If you want to go a step further, Windows lets you set up your own VPN server without installing third-party software . It's not as convenient as using a commercial service, but it gives you more control over who manages your data and how your home network is accessed.
The process is based on the old Incoming Connections tool in the Control Panel. To begin, go to Windows Settings and then to Network & Internet . From there, in Windows 10, go to "Status" and click on "Change adapter options." In Windows 11, go to "Advanced network settings" and select "More network adapter options."
The classic Control Panel window will open, displaying your network adapters (Ethernet, Wi-Fi, etc.). In that window, press the Alt or F10 key to bring up the classic menu if it's not already visible. Then, go to "File" and select "New Incoming Connection." This option allows you to configure Windows to accept connections from other computers over the internet.
A screen will appear displaying the system's user accounts. You can select existing users or create a new one to use when connecting to the VPN. For security reasons, it's highly recommended to create a dedicated VPN user account with a strong username and password, which you will then use on your client devices.
On the next screen, Windows will ask you how these users will connect. Make sure to leave the "Over the Internet" box checked , as this allows the VPN connection to be established from outside your local network, passing through the internet to your server computer.
A list of the network protocols and components for the incoming connection will then appear. It's important to select "Internet Protocol Version 4 (TCP/IPv4)" and click "Properties." This window allows you to decide which IP addresses will be assigned to VPN clients once they connect.
By default, Windows may attempt to assign IP addresses automatically, but it's better to tell it to reserve a specific IP address range for the VPN . Select the option that allows you to specify IP addresses and define a range within your local subnet. This sounds more technical than it is, but it can be solved by knowing your gateway IP address.
To find out, open the Command Prompt application and run the command ipconfig . Among the displayed data, you'll see a line with "Default Gateway," which will almost always be something like 192.168.0.1 or 192.168.1.1. This is your router's IP address.
In the VPN server's IPv4 properties, the first three numeric segments of your assigned IP addresses must match those of your router . For example, if your gateway is 192.168.1.1, you can reserve the range 192.168.1.20 to 192.168.1.30 for your VPN. This way, any client connecting to your VPN server will receive an IP address within that range.
Once you've defined the range, accept the changes and return to the network software screen. Everything is now ready, so simply click "Allow access" to allow Windows to create the incoming connection and activate the VPN server. From then on, your computer will be ready to receive external VPN connections, provided your router and firewall aren't blocking the traffic.
Open the port on the router and configure the Windows firewall
To allow devices outside your home or office to reach the VPN server, you need to open the corresponding port on your router and configure the Windows firewall to allow that traffic. Otherwise, any connection attempts from the internet will be blocked before reaching the server.
In most home setups, routers use the gateway IP address we mentioned earlier (something like 192.168.1.1 or 192.168.0.1). If you type that address into your browser's address bar, you can access the router's web interface . The initial username and password are usually printed on a sticker on the device itself, but for security reasons, it's highly recommended to change them.
Once you're inside the router, you need to look for the section related to "Port Forwarding" or "NAT" . The terminology varies depending on the manufacturer, but the idea is always the same: to define a rule that opens an external port and directs it to the internal IP address of the device running your VPN server.
The standard port for this type of connection in Windows is 1723. You will need to create a new rule specifying that TCP traffic to port 1723 should be sent to your server computer's private IP address (not the router's). If you don't know that IP address, use the ipconfig command again and look at the "IPv4 Address" line corresponding to your active network adapter.
In parallel, you need to adjust the Windows firewall so that it doesn't block remote access functionality. Go to Control Panel, then to System and Security > Windows Defender Firewall , and in the left column, click on "Allow an app or feature through Windows Defender Firewall."
Within that window, click on “Change settings” to modify the list. Then, in alphabetical order, find the entry called “Routing and Remote Access” and check both the private and public network boxes. By doing so, you will be authorizing that service to receive traffic through the firewall on both types of networks. Save the changes by clicking OK. If you want more tools to manage firewall security, you can review options for managing the Windows Firewall.
Some more advanced guides also recommend checking the network profile using PowerShell . By running it as administrator and using commands like Get-NetConnectionProfile and Set-NetConnectionProfile, you can ensure your local network is marked as "Private," which reduces firewall conflicts and prevents unnecessary blocks.
If you want your VPN server to be available as soon as you turn on your computer, it's a good idea to go to the Windows "Services" tool, locate the "Routing and Remote Access" service , open its properties, and set the startup type to "Automatic (Delayed Start)." This will ensure that Windows starts the VPN service reliably every time it boots up.
Manage dynamic IP and domain for your VPN server
There's a practical detail that's often overlooked: your router's public IP address is usually dynamic . This means your internet service provider can change it at any time (for example, when you restart your router), which would render the address you're using to connect to your VPN invalid.
A simple way to solve this is to use a dynamic DNS service, such as No-IP or similar . These services allow you to register a domain name (for example, “tuvpn.no-ip.org”) that will always point to your router's current public IP address, even when it changes.
The procedure is usually similar for all providers: first, you register on the website, choose your desired domain name, and then install a small client on your PC that acts as a VPN server . This client is responsible for notifying No-IP whenever your public IP address changes, so that the domain name is automatically updated.
Within your account panel for the dynamic DNS service, you'll need to ensure that the domain you created is selected and associated with the client installed on your computer. From then on, even if you restart your router and your public IP address changes, the client will update the information, and you'll always be able to connect by entering the same domain name in the VPN settings.
This is very useful because it saves you from having to check and share the new IP address every time it changes. In practical terms, your devices only need to know that fixed domain, the username, and the password you set for the VPN.
Connect to your VPN from Windows and other devices
Once you have the server up and running, the ports open, the firewall adjusted and (if you want) the dynamic domain configured, comes the most rewarding part: connecting to your VPN from other devices , both with Windows and from Android or iOS mobiles.
On a PC running Windows 10 or 11, the process is very similar to setting up any other VPN. Go to Settings, then Network & Internet > VPN , and click "Add a VPN connection." Under Provider, choose "Windows (built-in)," give the connection a name, and in "Server name or address," enter your router's IP address or domain name (or your server's IPv4 address if you're on the same local network).
In the authentication fields, enter the username and password you created specifically for the incoming VPN connection. Save the profile and then select the connection and click "Connect." If everything is configured correctly, you'll see the status change to "connected" in a few seconds, and your computer will begin using the VPN tunnel.
It's a good practice to then review the advanced settings of your VPN connection by accessing its properties through the Control Panel, under "Network and Sharing Center" and "Change adapter settings." There you can adjust the security and networking settings , disabling IPv6 if you don't need it, ensuring IPv4 is enabled, and, if applicable, going to "Advanced Options" to decide whether or not to use the VPN server's default gateway.
In the security section of that same window, verify that the VPN type and encryption methods match what you've configured on the server to avoid authentication or protocol errors. Once everything is set up correctly, simply click "OK" and test the connection again.
On Android and iOS mobile devices, the process is similar, although the interface differs. Each system has its own "VPN" section in the network settings, where you can create a new profile by entering the server address, VPN type, username, and password . The key remains the same: point to the correct IP address or domain and use the credentials you created on your Windows computer.
Use a provider's VPN service instead of setting up your own
If setting up a server, opening ports, and tweaking the firewall sounds too complicated, you have another option: using a commercial VPN through a Windows application . In this case, you don't have to maintain the servers yourself; you delegate that task to a specialized provider.
The market is highly competitive, with numerous services like NordVPN, CyberGhost, ExpressVPN, AVG Secure VPN, and many others. The process is always similar: you register, install the official app, log in, and choose a server in your desired country . The app then handles creating the tunnel, managing protocols, reconnections, and additional options such as the kill switch.
When choosing a provider, it's advisable to focus on three key points: the privacy and no-logs policy , the type and level of encryption they use (to avoid weak services), and the company's overall reputation, including the jurisdiction in which it operates and the technical support options it offers.
In practice, you simply download the Windows version of the application from their website or the Microsoft Store , run the installer, and follow the wizard. They often include free trial versions so you can test speed , stability, and ease of use before committing to a full subscription.
Once the app is installed, you choose a server (or let the VPN automatically select the fastest available one), activate the connection, and you're all set. At that point, all your internet traffic is routed through the commercial VPN , and you can switch virtual countries with a couple of clicks if you need to access geographically restricted content.
These applications typically include advanced features such as a kill switch (which cuts off your internet connection if the VPN drops) , support for various protocols (OpenVPN, WireGuard, etc.), automatic connection on open Wi-Fi networks, and additional options to prevent DNS or IPv6 leaks. All of this reduces the risk of data leaks that you might encounter if you manually configure the VPN and make a mistake.
On the other hand, you're completely dependent on that provider: all your traffic passes through their servers , so you should choose one with a good reputation and clear no-logs policies. Free VPNs, in particular, are often funded by exploiting usage data or injecting advertising, so they're not the best idea if true privacy is your priority.
Ultimately, setting up your own VPN on Windows or using a commercial service are two different paths to similar goals: a more secure, encrypted connection and better control over your information . The choice depends on whether you prefer absolute control and a bit more technical effort, or convenience and a turnkey solution in exchange for relying on a third party.
